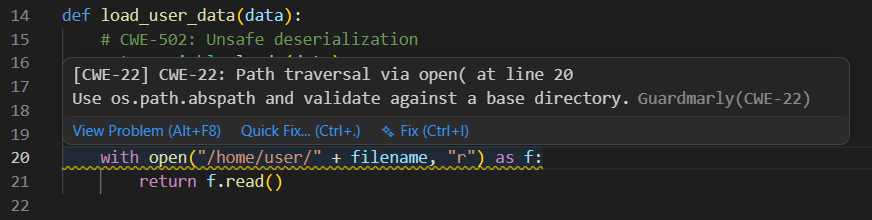
SAST scanner inline in your editor. Detects IDOR, missing authorization, SQL injection, XSS, path traversal, and 30+ more CWE types — runs locally on your machine.
Features
- 🔍 Real-time scanning — findings appear inline as you type
- 🛡️ IDOR detection — catches authorization bugs other tools miss
- 📊 Trace-backed findings — see the full taint path from source to sink
- 🌐 5+ languages — Python, JavaScript/TypeScript, Go, Java, C#, and 35+ more
- 📋 SARIF output — one-click export for GitHub Code Scanning
- 🔒 Runs locally — scans files on your machine, no cloud required
- ⚡ Auto-detects guardmarly CLI — works with pip, pipx, or python -m
Installation
Install from the VS Code Marketplace or:
code --install-extension guardmarly.guardmarly
Usage
- Open any Python, JavaScript, Go, Java, or C# file
- Guardmarly scans automatically on open and on save
- Findings appear as inline diagnostics with severity badges
- Run
Guardmarly: Scan workspacefrom the command palette for a full scan
Settings
| Setting | Default | Description |
|---|---|---|
guardmarly.enabled |
true |
Enable/disable scanning |
guardmarly.failOn |
"high" |
Minimum severity to highlight |
Commands
| Command | Description |
|---|---|
Guardmarly: Scan file |
Scan the active file |
Guardmarly: Scan workspace |
Scan all files in the workspace |
See CLAIMS_AND_EVIDENCE.md for benchmark methodology and measured results.